Security and compliance for payment businesses in Canada and the US
Be ready for the
security review
behind your next
partnership.
A bank, acquirer or enterprise customer needs evidence that your business meets its requirements. Your team needs clarity on what applies, what is missing and what to do next.
Blaecwood helps you assess readiness, address control gaps and prepare evidence for partner reviews and independent assurance.
Who We Help
Built for payment
businesses with a
requirement to meet.
You have a compliance or risk owner. You also have competing deadlines, evidence spread across teams and a partner asking questions that need supported answers. We work with payment businesses, typically with 20 to 200 employees, facing a specific commercial or compliance requirement.
A relationship depends on your documentation
A new relationship, renewal or expansion depends on security documentation, evidence or an applicable PCI validation requirement. You need a clear scope and a practical plan.
An enterprise customer has asked for proof
An enterprise customer has requested a SOC 2 report, completed questionnaire or supporting evidence. You need to establish what they will accept and prepare accordingly.
The date is set and readiness is unclear
Your audit or assessment is approaching. Policies exist, but evidence is incomplete, remediation is unfinished or ownership is unclear. You need an accurate view of readiness.
What Applies
Know what applies
before building
the programme.
Requirements depend on your activities, data, jurisdiction and agreements. We document the source of each requirement and distinguish three categories.
What the law requires of you
For Canadian operations, we assess the applicability of PIPEDA and relevant provincial privacy laws.
For US operations, we assess applicability of the FTC Safeguards Rule, 16 CFR Part 314, and relevant state privacy requirements, including thresholds and exemptions.
Each identified obligation is linked to its legal source. Unresolved interpretations are flagged for legal review.
What your agreements impose
PCI DSS requirements depend on your payment activities and the requirements imposed through your acquirer, payment brand or other agreements.
We identify the imposing agreement or scheme rule and assess the relevant scope against PCI DSS v4.0.1. Its future-dated requirements became effective on 31 March 2025.
What your customers will accept
SOC 2 reports, security questionnaires and other evidence requests are tied to the specific customer or partner requirement.
SOC 2 readiness uses the 2017 Trust Services Criteria, with revised points of focus published in 2022, with scope agreed for the engagement.
The result: a sourced requirements map, agreed priorities and a clear evidence plan.
How It Works
From unclear requirements
to organised readiness.
We review your business activities, systems and partner requests. You receive a requirements map and prioritised gaps, with assumptions and unresolved questions clearly identified.
We develop or update the policies and procedures required by the agreed scope, identifying the framework and version used.
Your team owns implementation. We help assign responsibilities, clarify requirements and review progress.
We define the evidence needed, coordinate collection and check relevance, completeness and traceability before external review.
Evidence stays in a central, access-controlled, versioned workspace licensed by your business in your own name. Blaecwood accesses it through agreed permissions and does not maintain a separate evidence repository.
Our review supports readiness. It does not constitute an independent opinion on control effectiveness.
Where SOC 2 is required, we help you shortlist an eligible independent CPA firm and coordinate preparation and evidence requests. The firm retains responsibility for the examination and report.
Where PCI validation is required, we help coordinate the applicable self-assessment, approved scanning vendor or qualified security assessor route. Blaecwood does not issue the resulting external assurance.
After the initial engagement, ongoing evidence reviews, remediation tracking and renewal preparation can be agreed under a separate scope.
The initial engagement sets out deliverables, responsibilities, fees and completion criteria. Any continuing service is agreed explicitly.
Start Here
Start with the
requirement in front
of you.
Bring the partner request, questionnaire, assessment deadline or control concern that prompted the conversation.
We will discuss your business, identify what needs clarification and outline a suitable next step.
Scope, timelines, client responsibilities and any external assurance costs are agreed before work begins.
About
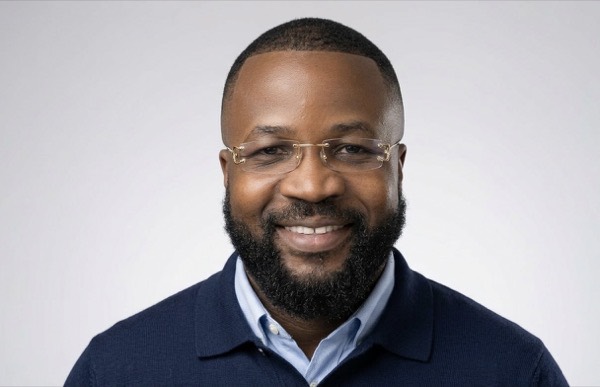
Blaecwood helps payment businesses connect security and compliance work to the requirements behind customer and partner relationships.
Founded by Kehinde Bade in Toronto, the practice combines practical security work, compliance readiness and evidence coordination.
Kehinde holds the CISSP with the ISSAP architecture concentration, the CCSP, and an MSc in Digital Forensics.
Our approach is straightforward: establish what applies, identify the gaps, organise the work and prepare supported answers for the people reviewing your business.
Sourced requirements Every obligation traced to its legal, contractual or customer source
Practical remediation Prioritised gaps, assigned responsibilities, reviewed progress
Evidence you control Held in a workspace licensed by your business in your own name
Assurance stays independent We coordinate the examination; we do not issue it
Your next review
starts with a clear plan.
Tell us what your bank, acquirer, customer or assessor
has requested.
Book a readiness conversation
Choose a time below. The calendar is requested from Cal.com only once you ask for it, so nothing third party loads before then.
Loading the booking calendar.
Prefer a separate tab? Open the booking page on Cal.com.